VigilMFA
Vigil / 2026
Clerk × Supabase
A separate experiment
The first build used Better Auth, Turso and Resend. This one moves identity to Clerk and the audit trail to Supabase.
A passwordless MFA console where every verified state change is written to an append-only ledger.
01 / Premise
Most MFA demos stop at the QR code. The interesting part starts after the first code is accepted.
A password is a promise.
A second factor is proof.
Vigil treats enrollment as a state change worth recording: who enabled what, when the server last checked, and whether Clerk and the ledger agree. The UI is quiet. The record is not.
03 / Sequence
Four movements. No shortcut through the second one.
- 01 / First
First, prove the inbox.
Enter your email. Clerk sends a six-digit code to the verified address. Nothing else is asked for.
- 02 / Then
Then, open the authenticator.
Scan the QR code once. Type the rotating six-digit code to prove the secret landed on your device.
- 03 / Now
Now, the session is gated.
Without a verified second factor, the console routes back to setup. There is no skip control.
- 04 / Finally
Finally, leave a record.
The server re-reads your MFA state from Clerk, then writes the verified snapshot to Supabase.
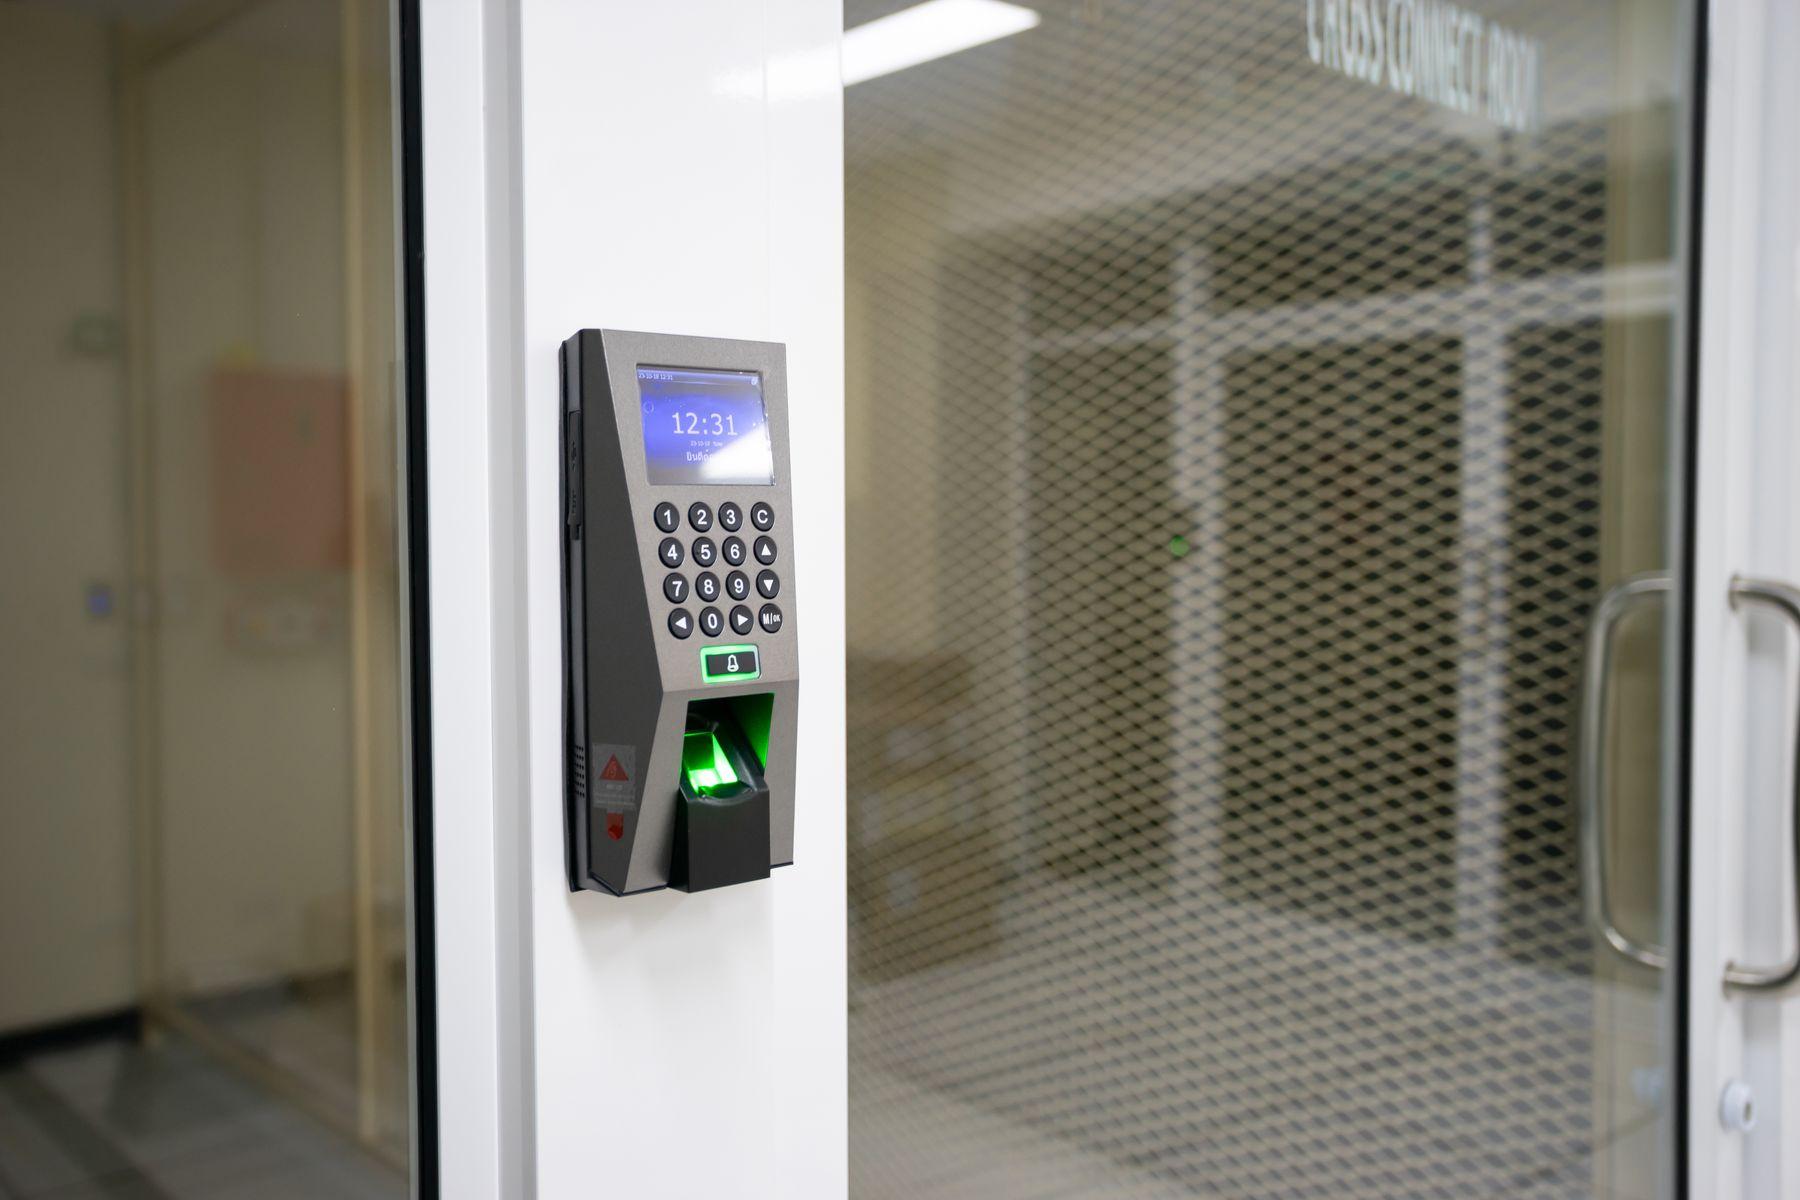
04 / The physical layer
Small habit.
Permanent record.
A fingerprint scanner is not a TOTP code. The analogy is the point: a second factor should be a physical act, not another password.
05 / The record
Built by people.
Checked by machines.
Vigil is a deliberate second experiment. The first build used Better Auth, Turso and Resend. This one moves identity to Clerk and the audit trail to Supabase. Same brief, different architecture.
Read the sourceIndeep Kour
Product direction, interface, original MFA experiment
The original build lives in a separate repository and keeps its Better Auth + Turso + Resend stack. Vigil is not a migration of that code; it is a second answer to the same brief.
Two builds / one brief
06 / Questions
Worth asking.
The honest version of each answer, including what is deliberately left out of this build.
01Does Vigil store my authenticator secret?
02What exactly is in the audit log?
03Can I run the console without a Supabase project?
04Why Clerk and Supabase instead of Better Auth and Turso?
05Is MFA enforced by the app or by Clerk?
06What happens if I lose my authenticator?
07Is this a production-ready compliance product?
07 / The gate
Vigil
Are you
Email code first. Authenticator second. The whole verified state on the record.